Skip to content
Engaze

Security

Your data, where you can point at it.

Every system we build can run inside your own office, on a server you own, reachable only from your own network. When it runs with us instead, here is exactly what we do and what crosses the line.
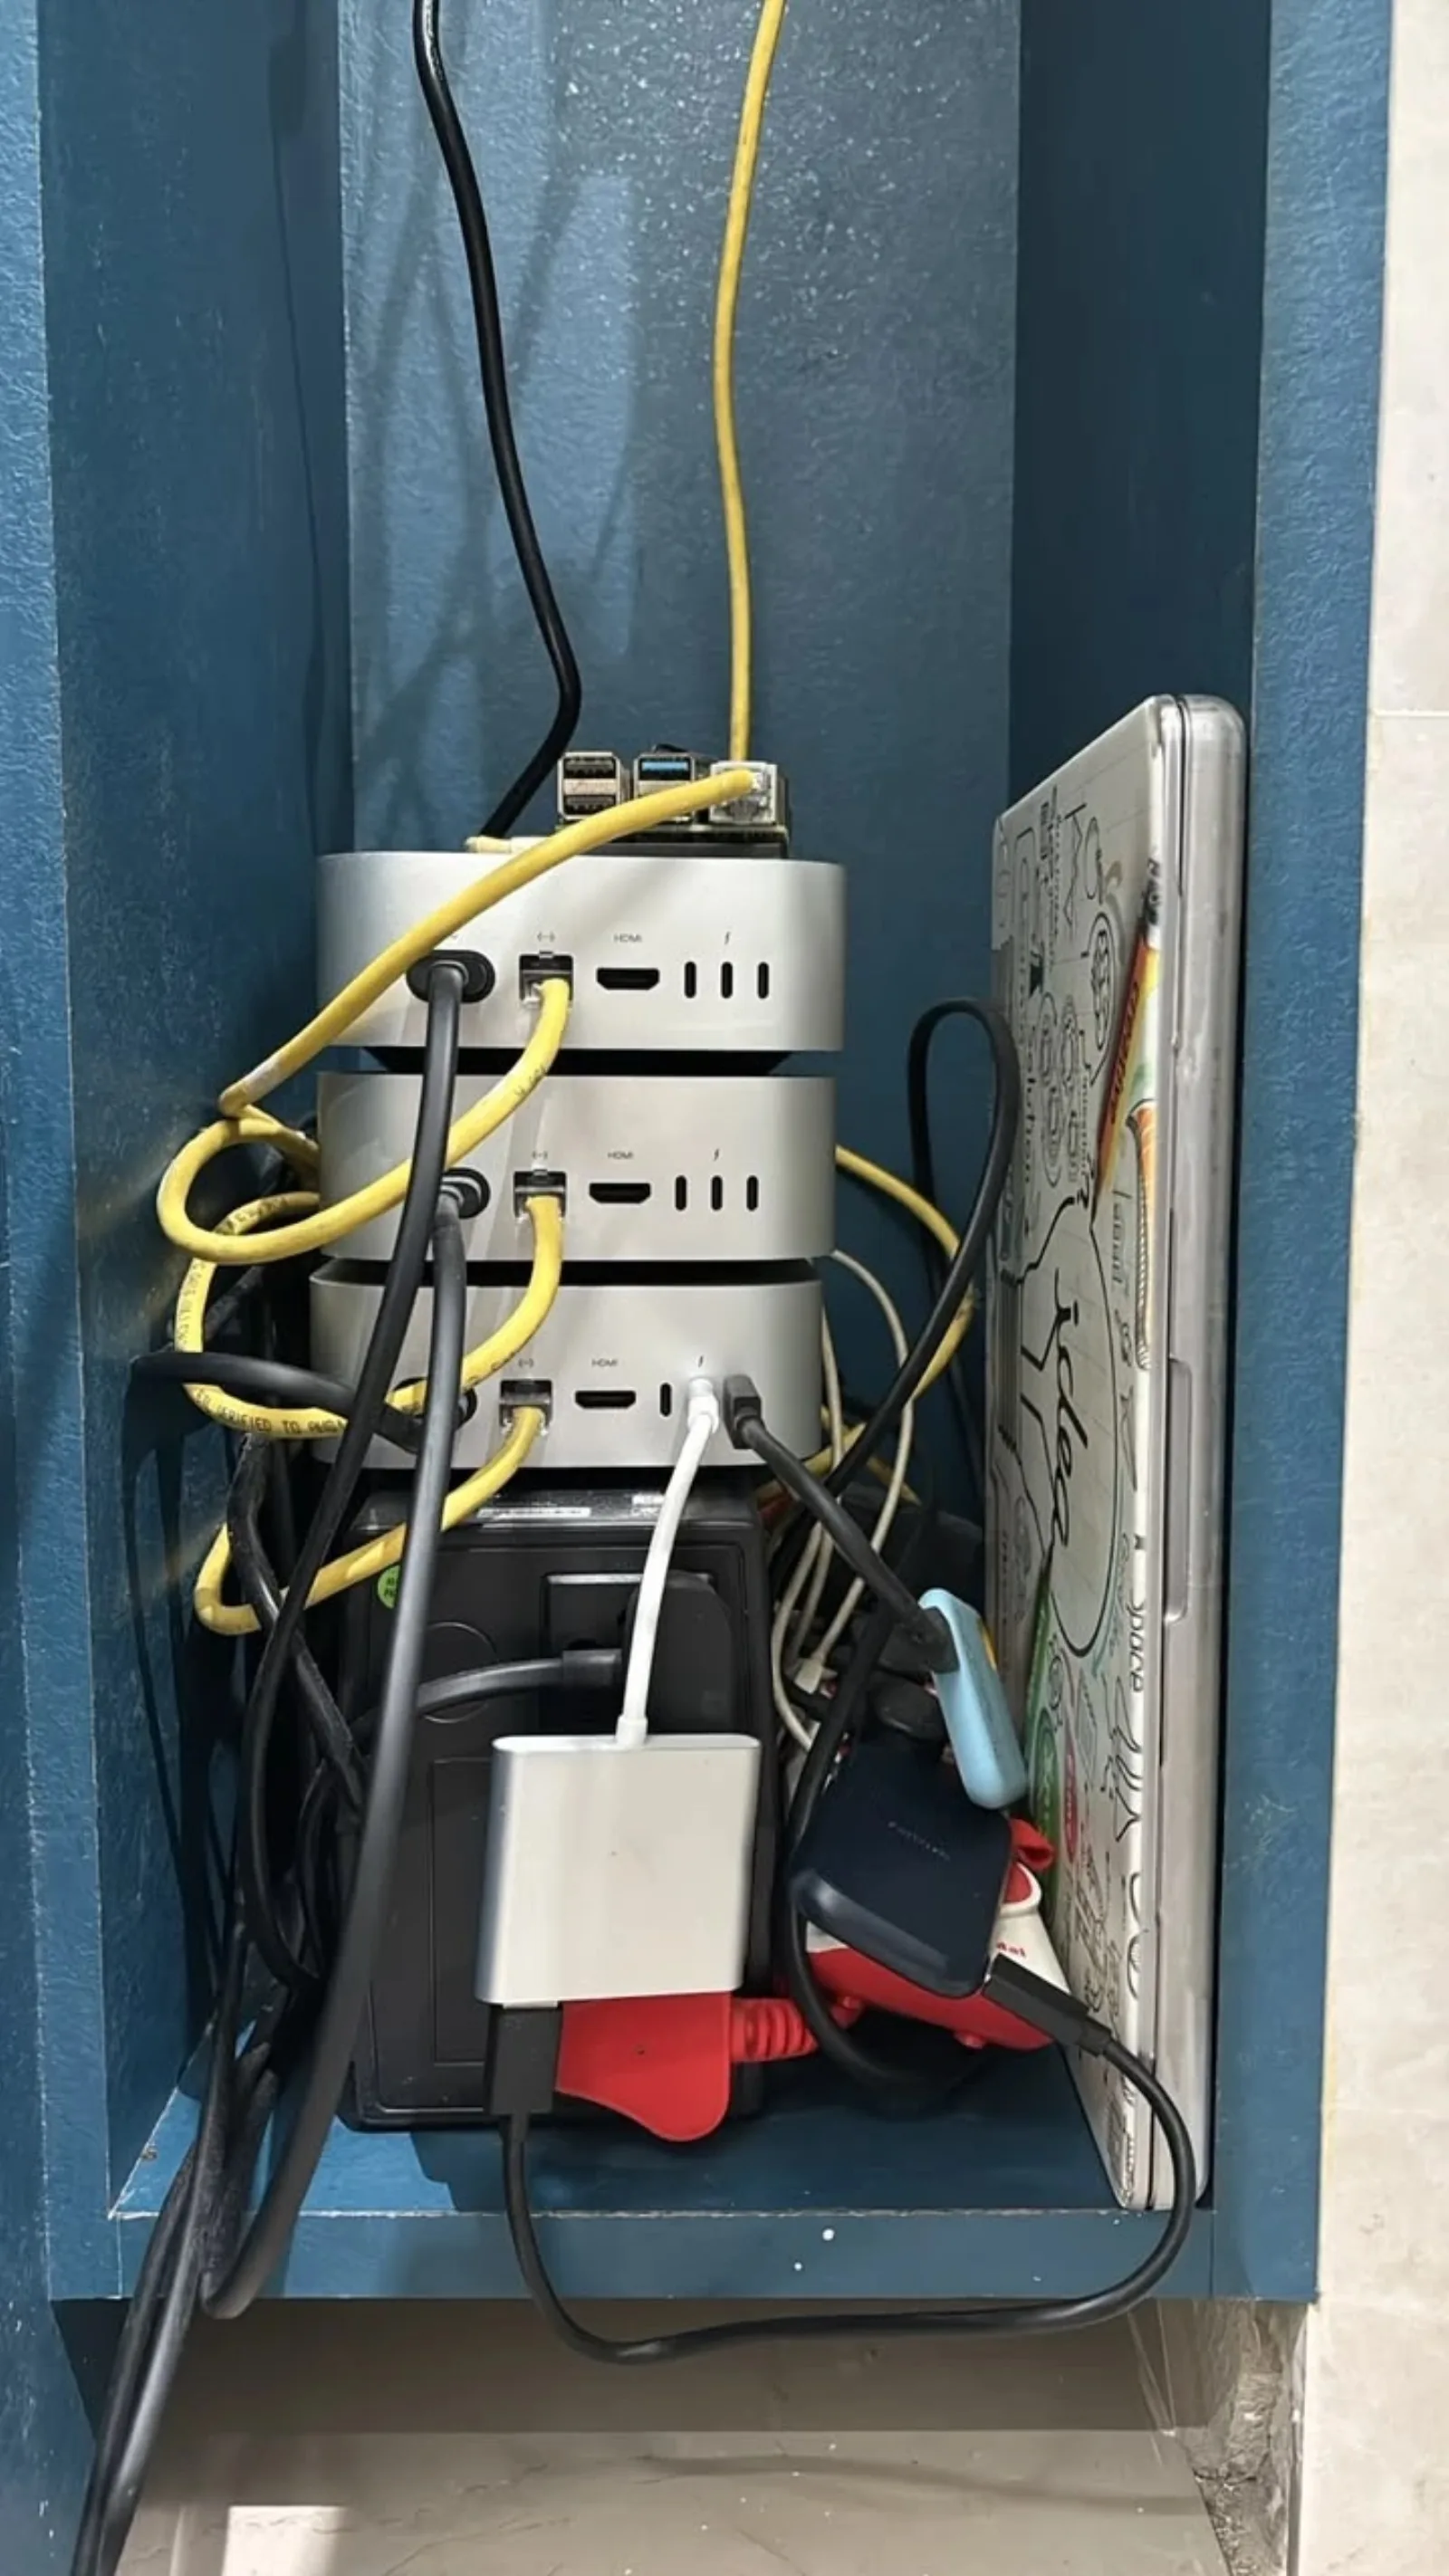
The Mac minis Engaze's hosted systems run on, in a cupboard in Mumbai

Where it runs

Pick where your system runs.

Inside your office

Factories, CA firms, anyone with confidential records

A small server (or a VM on a machine you already have) inside your premises. The system is reachable only on your own Wi-Fi or LAN; from outside, only through a VPN you control.

What leaves
Nothing, unless you switch on a specific integration (a courier, a payment gateway, an AI model) and we document what it sends.
What you hold
The server, the database, the backups, the keys.
  • Works when the internet is down
  • No data leaves the building
  • We update over a VPN session you approve

The boundary

What crosses the line, and when

A boundary is only real if you can see what goes through it. These are the only things that do.

  • Software updatesInto your system
    When
    When you ask for a release, or on a schedule you set
    Who approves
    You
  • Support accessInto your system, logged
    When
    Only during a support session you open
    Who approves
    You, each time
  • Integrations (courier, payments, Tally, email)Out, to that provider
    When
    Per transaction, only the fields that integration needs
    Who approves
    Agreed at setup; documented
  • AI model callsOut, to the model provider, or none with a local model
    When
    Only for steps you switched on; the exact fields are listed
    Who approves
    Agreed at setup; documented
  • BackupsOn the same server today; off-site copy planned
    When
    Hourly and nightly
    Who approves
    Set at setup
  • Analytics or telemetryNone by default
    When
    Never, unless you ask for usage reports
    Who approves
    You

Practices

Practices we follow on the systems we run today.

  • Access is per person, and it ends

    Every user has their own login; roles decide what each one can see and do.
    • Access for leavers is removed the day they leave; a quarterly list of who can do what is yours to review.
  • Every change is recorded

    An audit trail of who changed what, when, from where, on every record that matters.
    • Deletions are soft where the law or your auditor may want the history back.
    • Admin actions, support sessions and deployments are logged too.
  • Keys and server access

    Keys are rotated when a person leaves or a device is lost.
    • Servers are reached by key-based SSH over a private network, never a password on an open port.
  • Encrypted in transit

    HTTPS everywhere, including inside your office network.
    • Mobile apps talk to the server only over TLS with certificate checks on.
  • AI handles only what it is told to

    Each AI step lists the exact fields it sends and to which provider; you sign off the list.
    • Where confidentiality demands it, the model runs on your own machine and nothing leaves.
    • Nothing you give us is used to train any model, ours or anyone's, without a written agreement.
  • Built to survive the bad day

    Rate limits, input validation and honeypots on the forms we build.
    • A tested restore, not just a backup: we restore and compare every week on the systems we host.

Support

Support tickets are tracked until they are closed

A ticket is never lost in a chat. Each one has a number, an owner, a status you can see, and it is closed only when you say the problem is gone.

  1. Open

    From inside the app, by email, or by message. It gets a number within minutes.

  2. Triage

    Classified by urgency the same day. Anything that stops work is worked on first.

  3. Fix

    Investigated, often with an AI agent reading logs and reproducing the fault, then fixed by us and reviewed before it ships.

  4. Verify

    You confirm it is gone. If not, it reopens.

  5. Close

    Closed with a note of what changed. The log of every ticket is yours.

Remote access to your system happens only inside a support session you open, and it is logged.

What we do not have

  • No SOC 2 or ISO 27001 certificate. Engaze is a small company; the practices above are real, the audit badge is not something we can honestly claim yet.

  • No 24×7 phone line. Tickets are answered during Indian working hours, and anything that stops work is handled the same day.

  • No off-site backup yet. Backups of the systems we host sit on the same server today; an off-site copy is planned.

  • Not every admin account on the systems we run has two-factor sign-in yet.

  • No promise that nothing can ever go wrong. Nobody can honestly make one. We can show you the backups, the logs, the access list and the restore test, and let you keep all of them.

Found a security problem in anything we run? Write to prerak@engaze.in with "security" in the subject. You will get a reply from a person, and credit if you want it.

Tell us what needs solving.

Three minutes, four questions. You will hear from Prerak himself, usually within a working day.

Start a project